AUDIT TRAIL
Everything evidenced, everything checkable.
From the moment an exception is found to the moment it is remediated, and every change made along the way, SOXLayer keeps a record built to hand to your external auditor.
DEFICIENCY LIFECYCLE
From exception to closed, with nothing skipped.
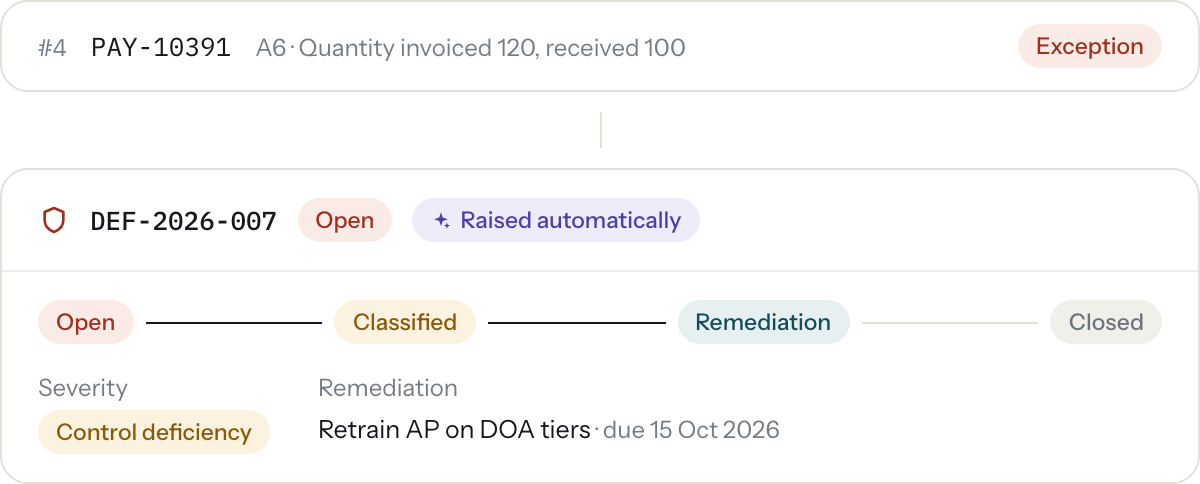
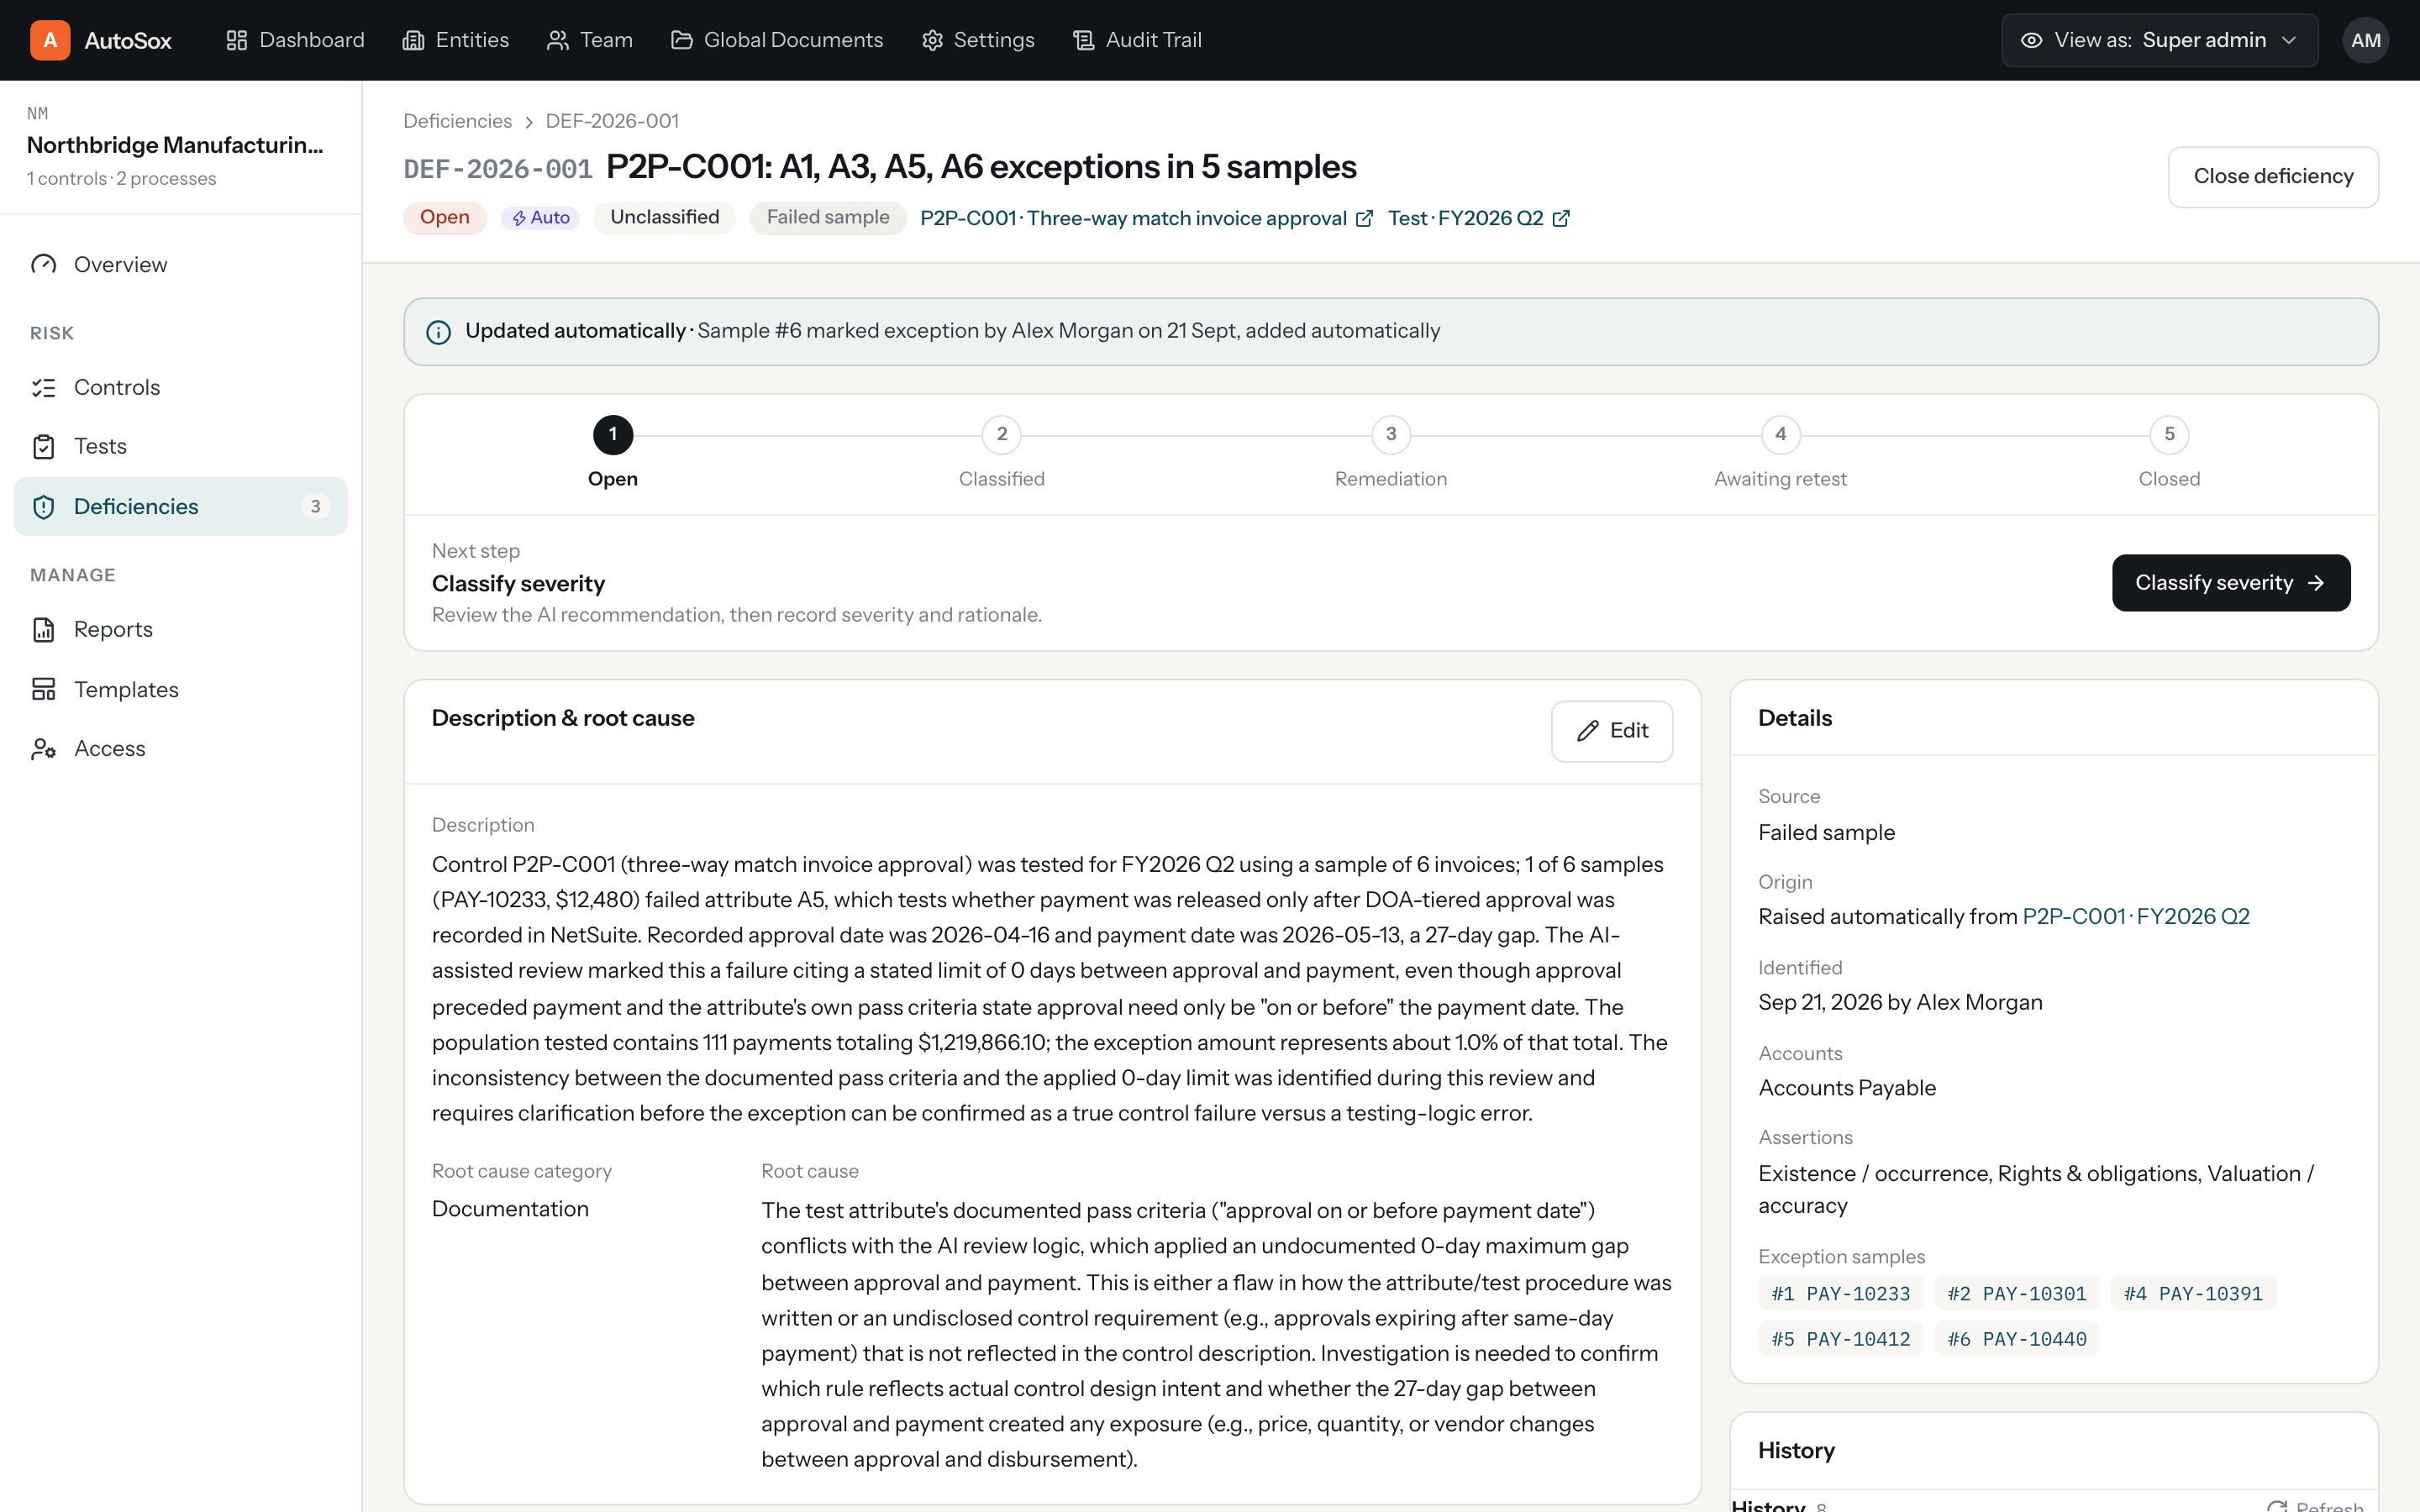
A sample marked as an exception raises a deficiency automatically, linked back to the test and the samples behind it. Severity is classified as a control deficiency, a significant deficiency or a material weakness, and each one carries a root cause, remediation items with due dates, and a lifecycle: Open, Classified, Remediation, Closed.
AUDIT LOG
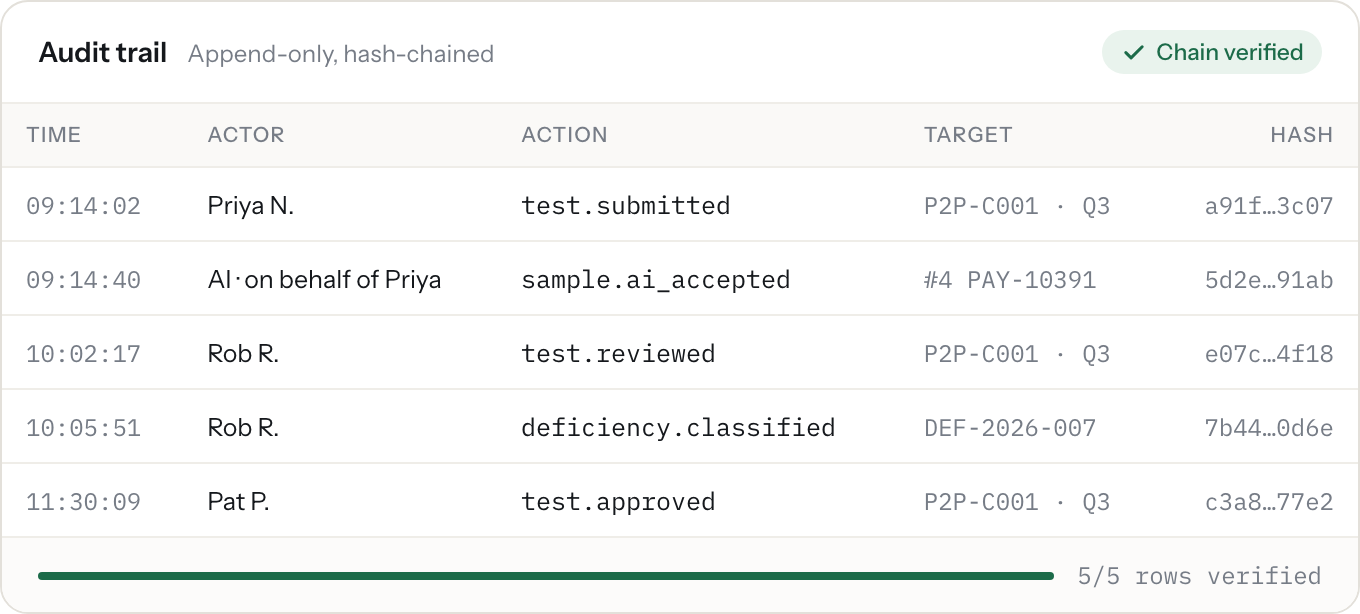
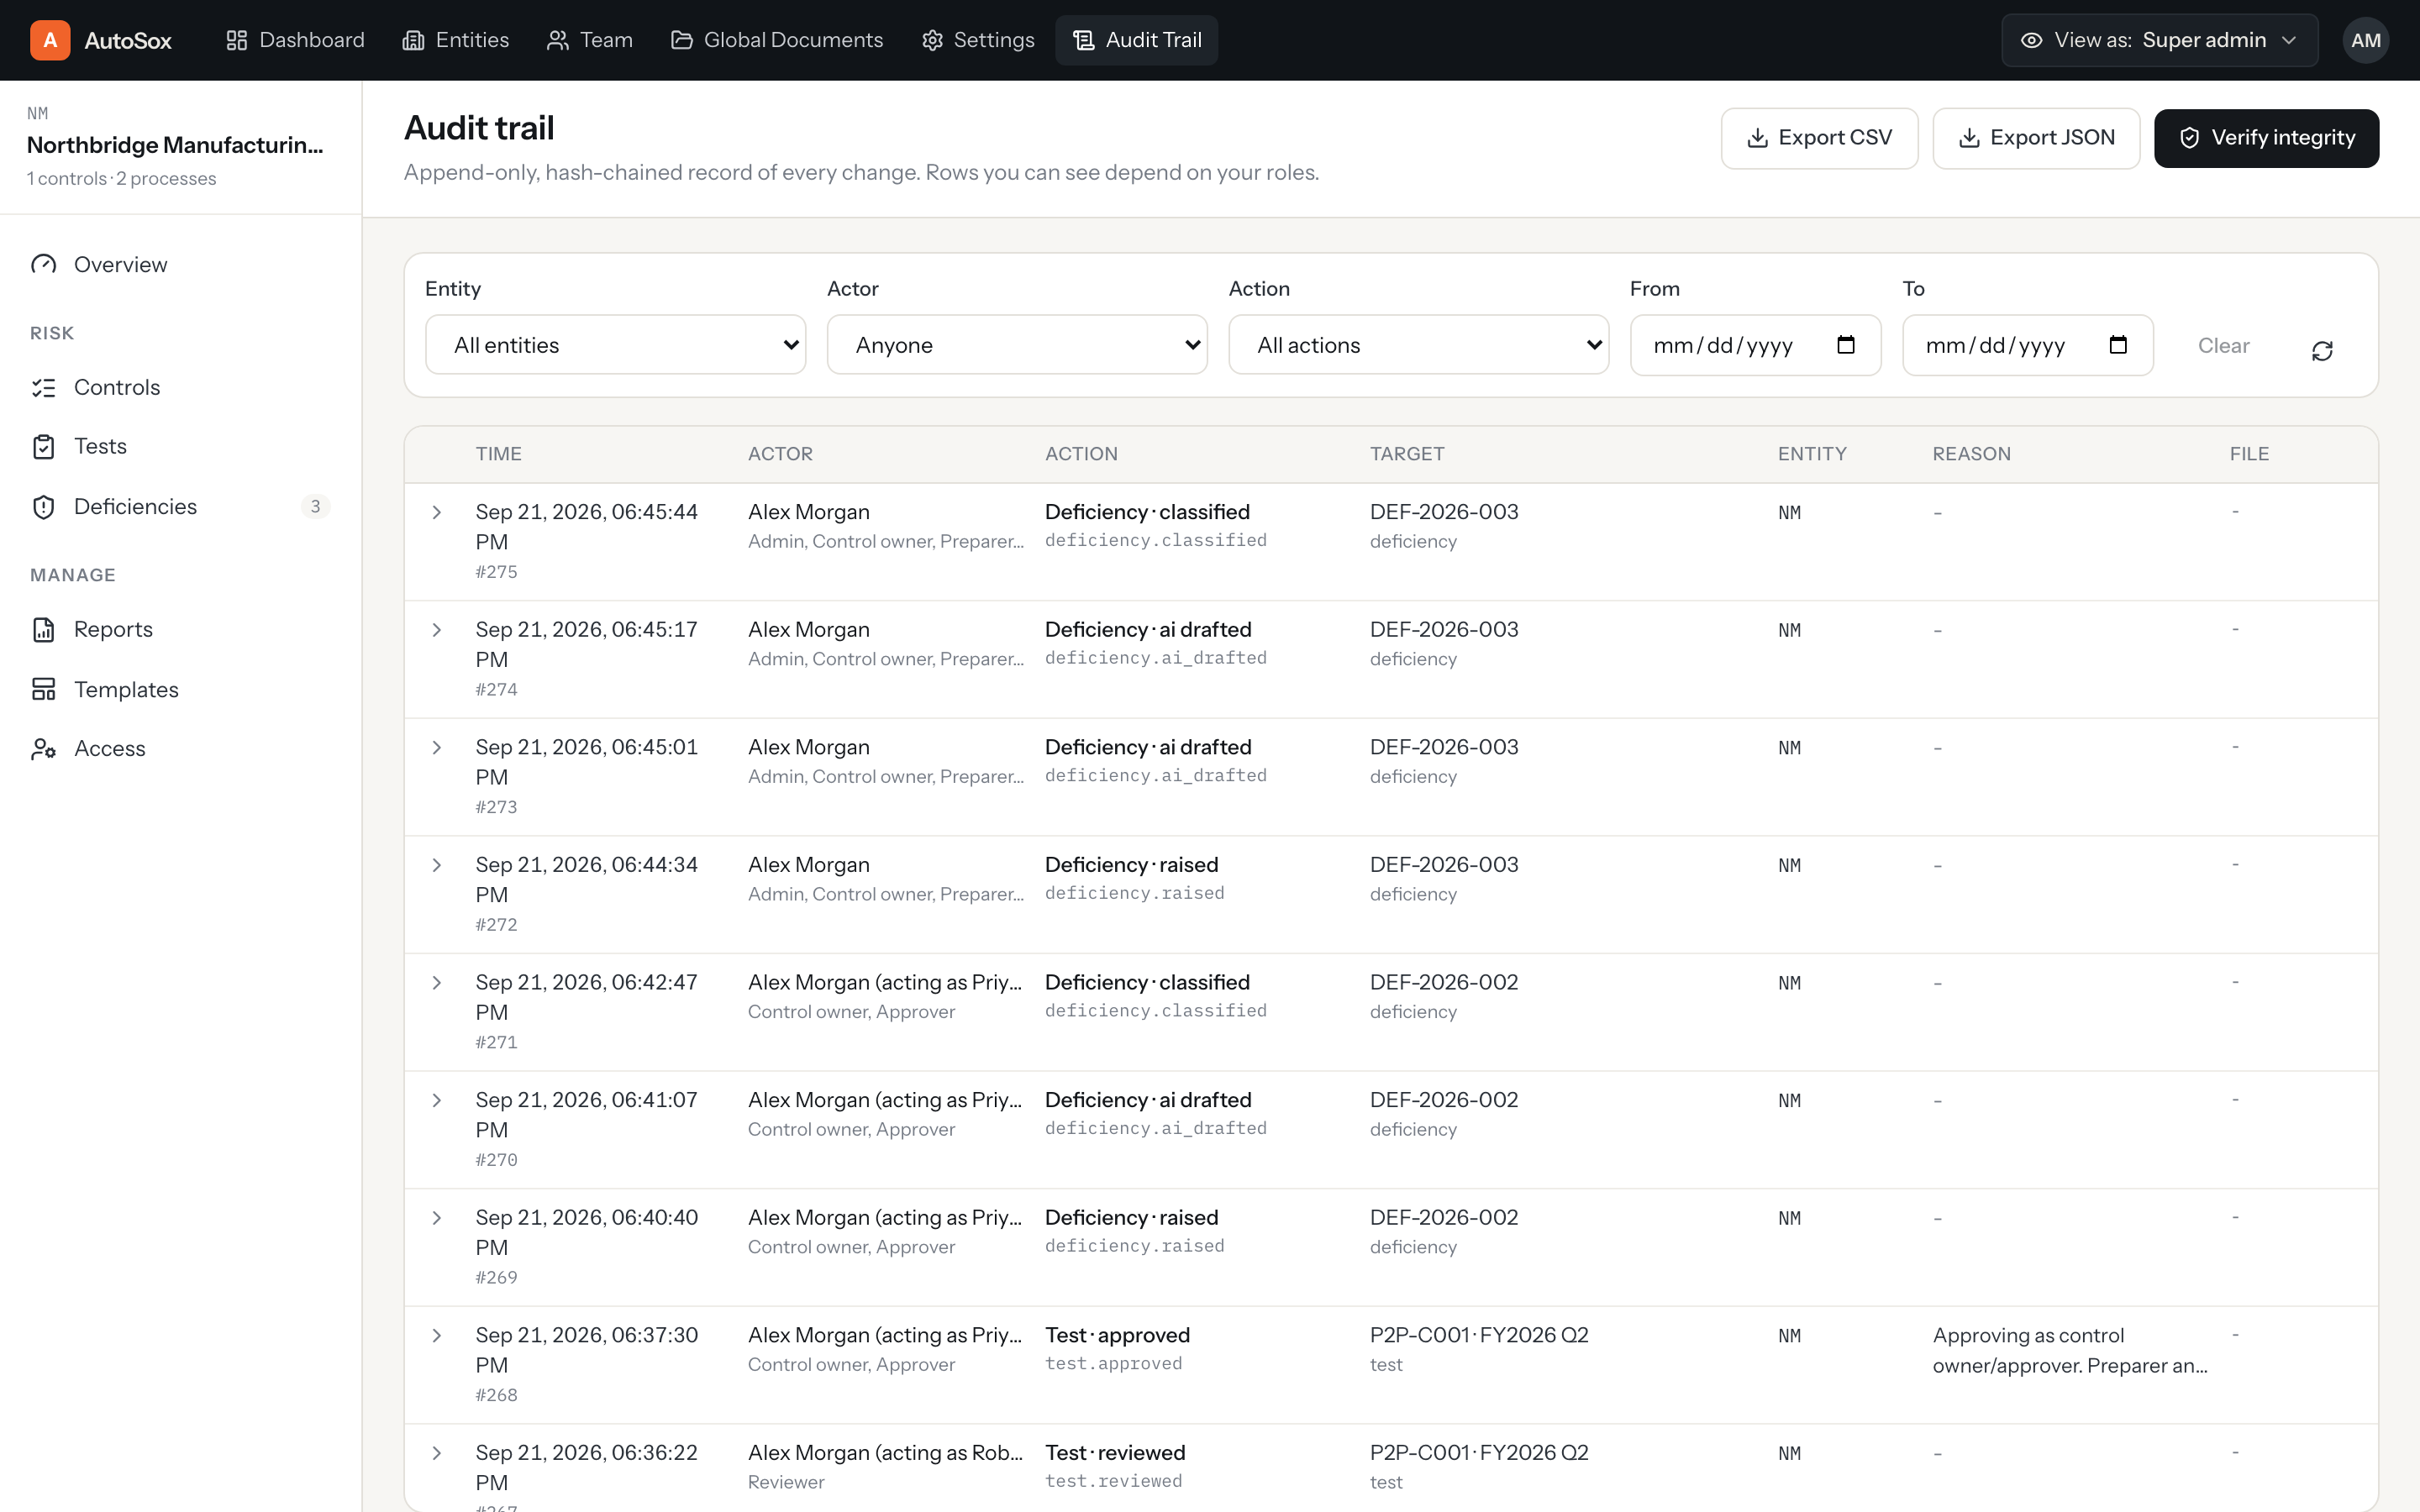
Append-only, hash-chained, and verifiable in one click.
- Who, what, when, before and after, and the reason for the change
- Filter by entity, actor, action and date
- Export as CSV or JSON
- "Verify integrity" checks the hash chain in one click
DOCUMENTS
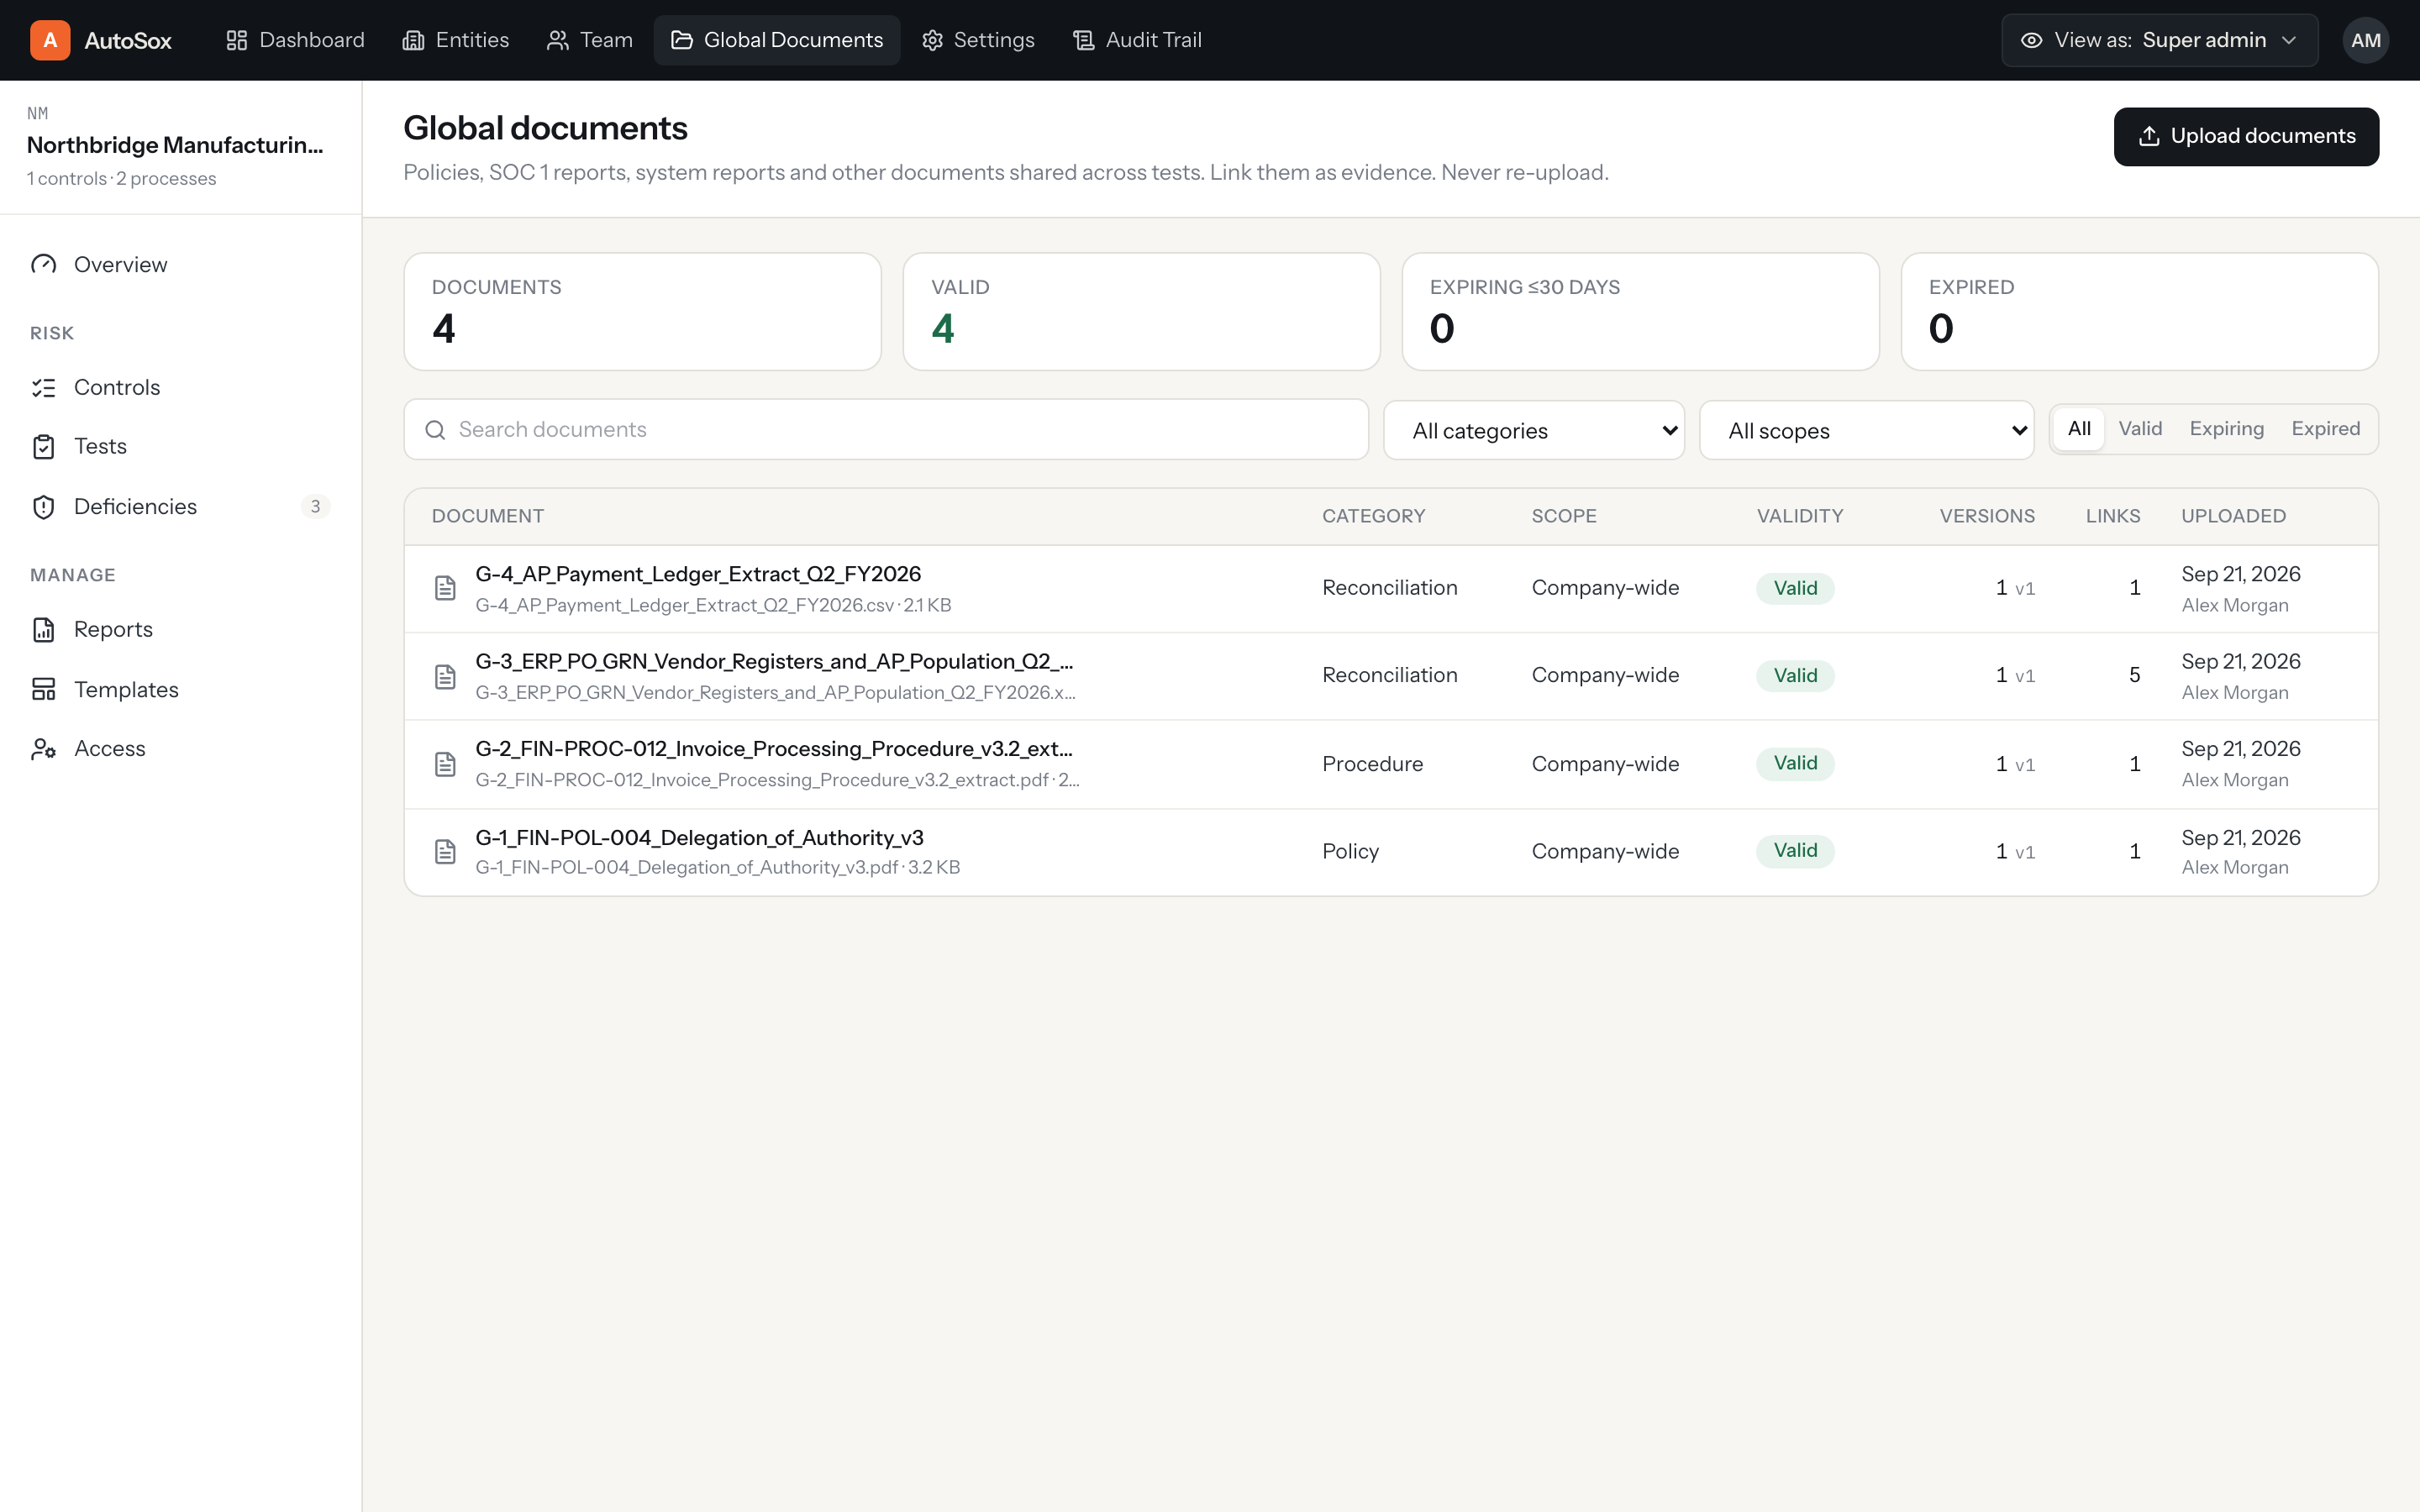
The documents behind your controls, kept current.
Global documents carry validity and expiry tracking with versioning, so every control links to the exact document version that was in force when it was tested.
TEAM
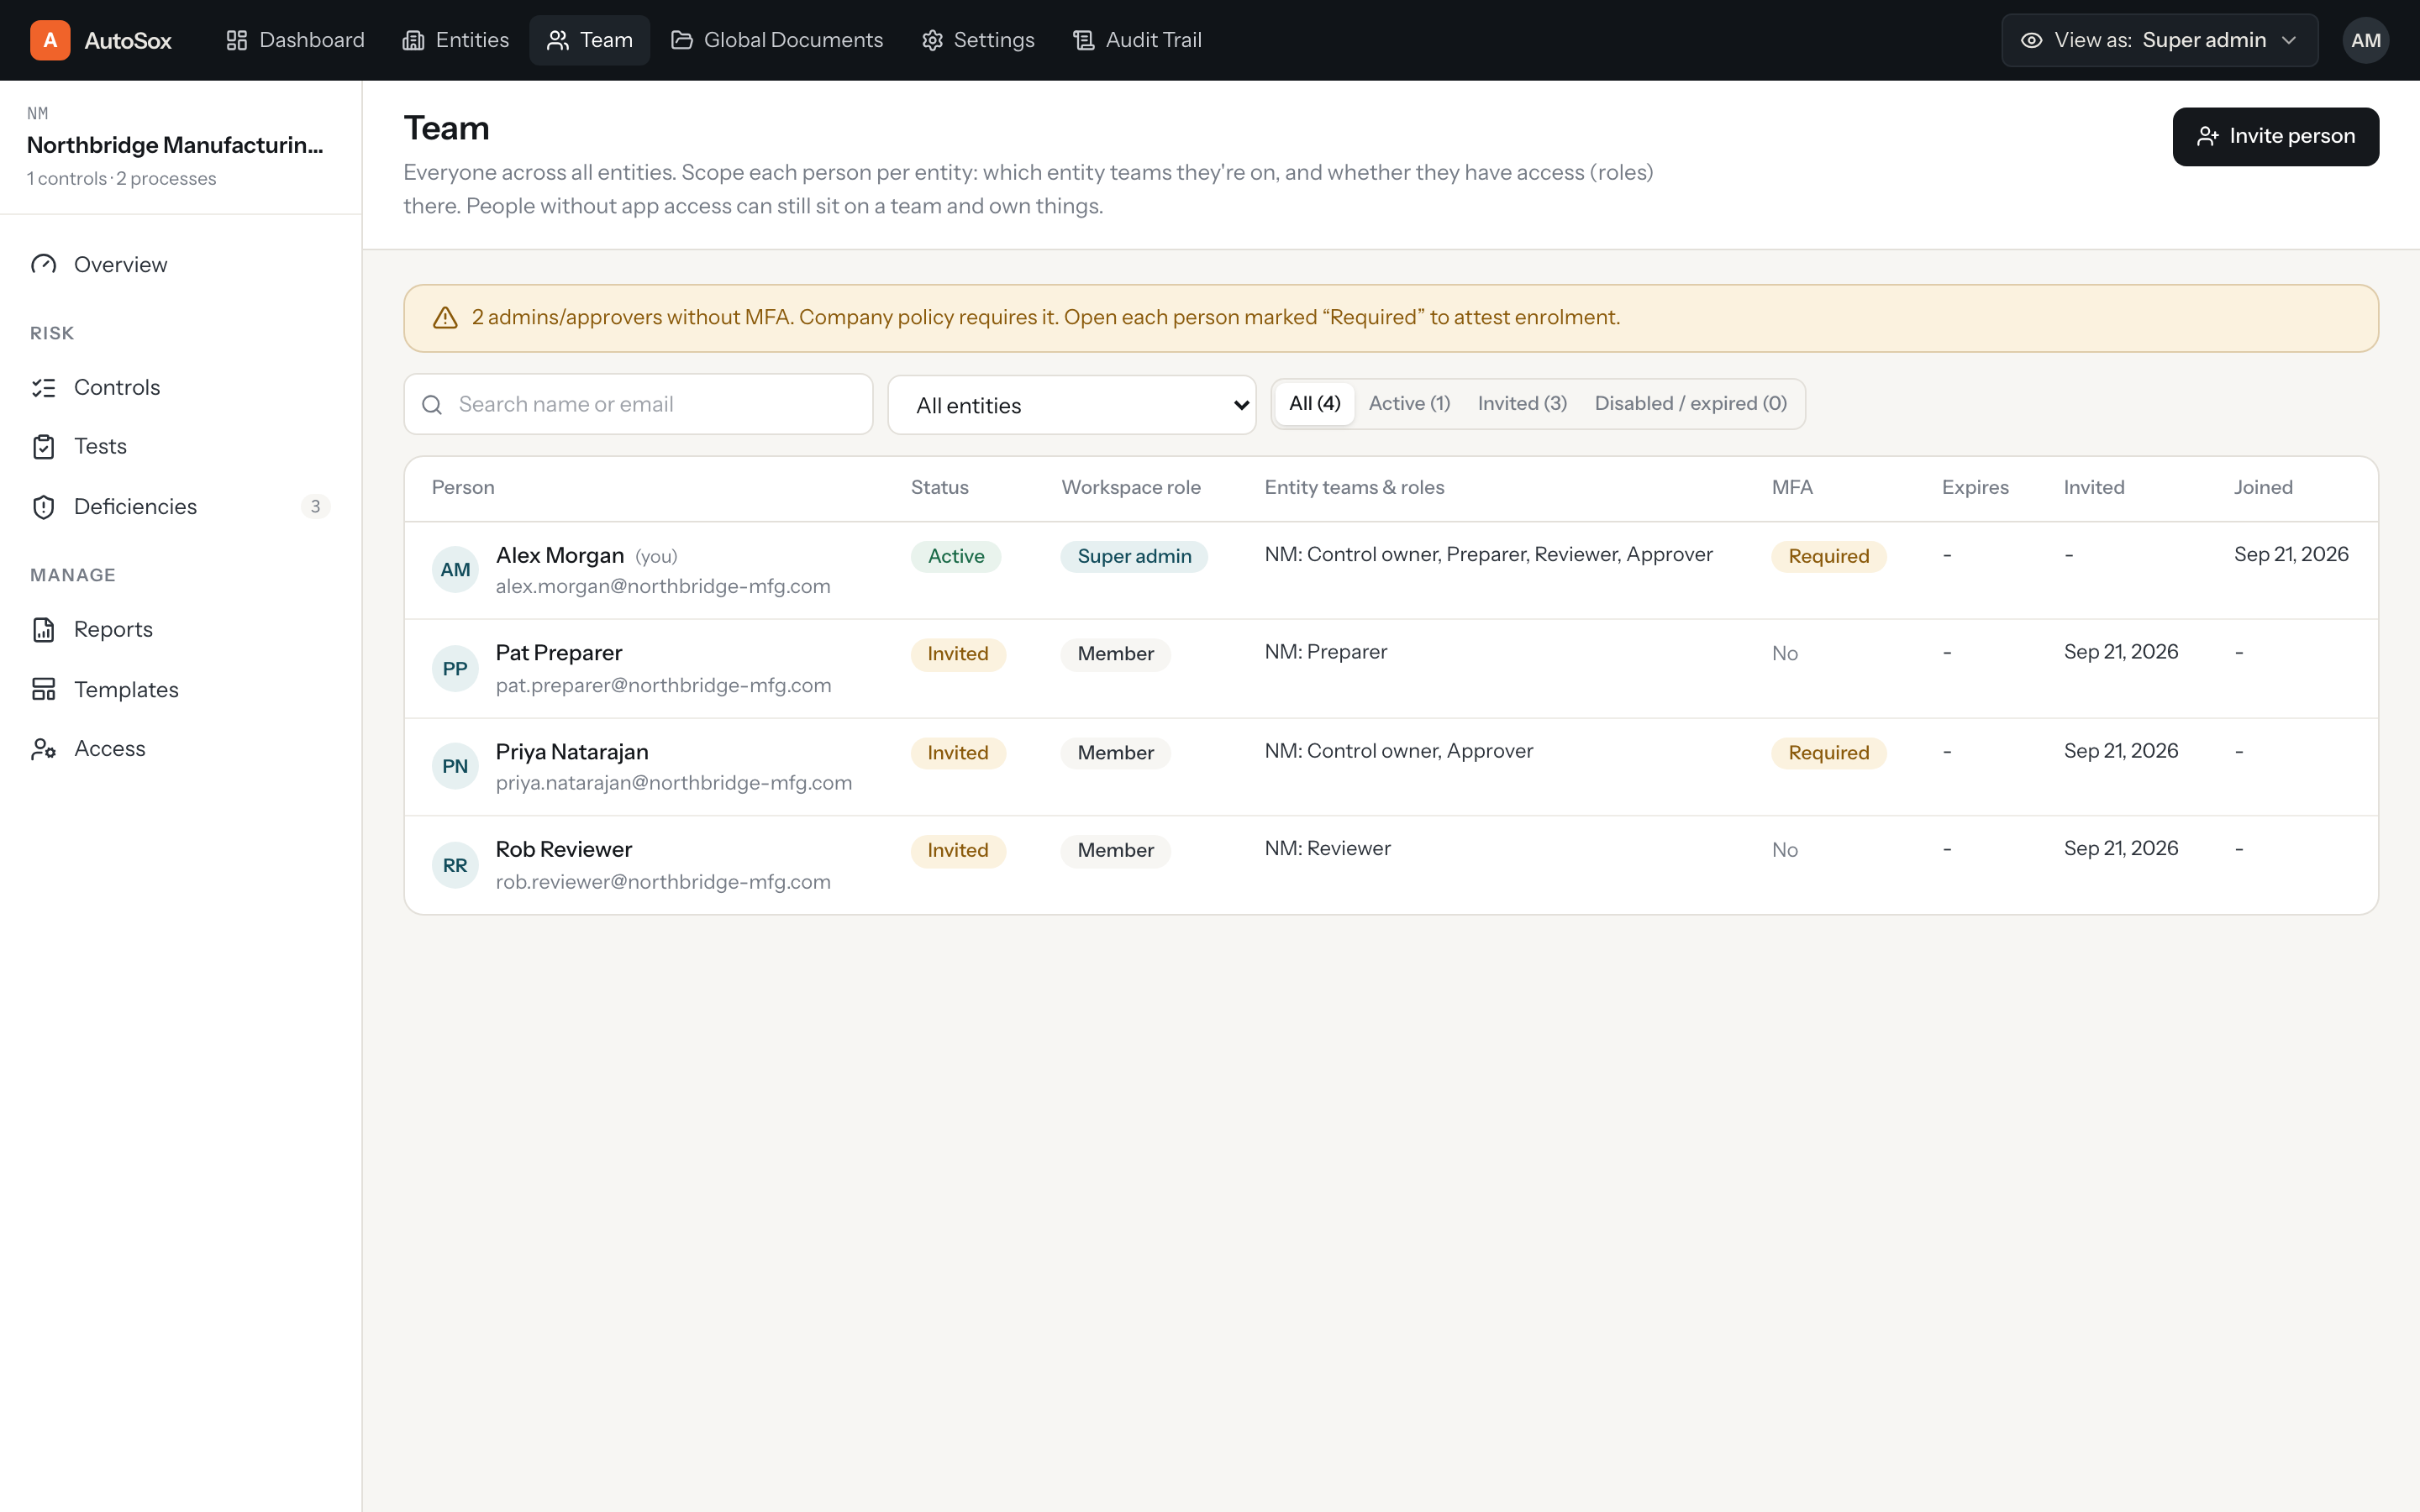
Who can see, test, review or approve, entity by entity.
Team members are scoped per entity with a clear role, and the MFA policy banner flags any admin or approver who has not turned on multi-factor authentication.
Start your 14-day free trial.
Bring one control and its evidence. See the AI test it in minutes.