SECURITY
How SOXLayer protects your data.
This page describes what the product does today. We keep it limited to what is actually built.
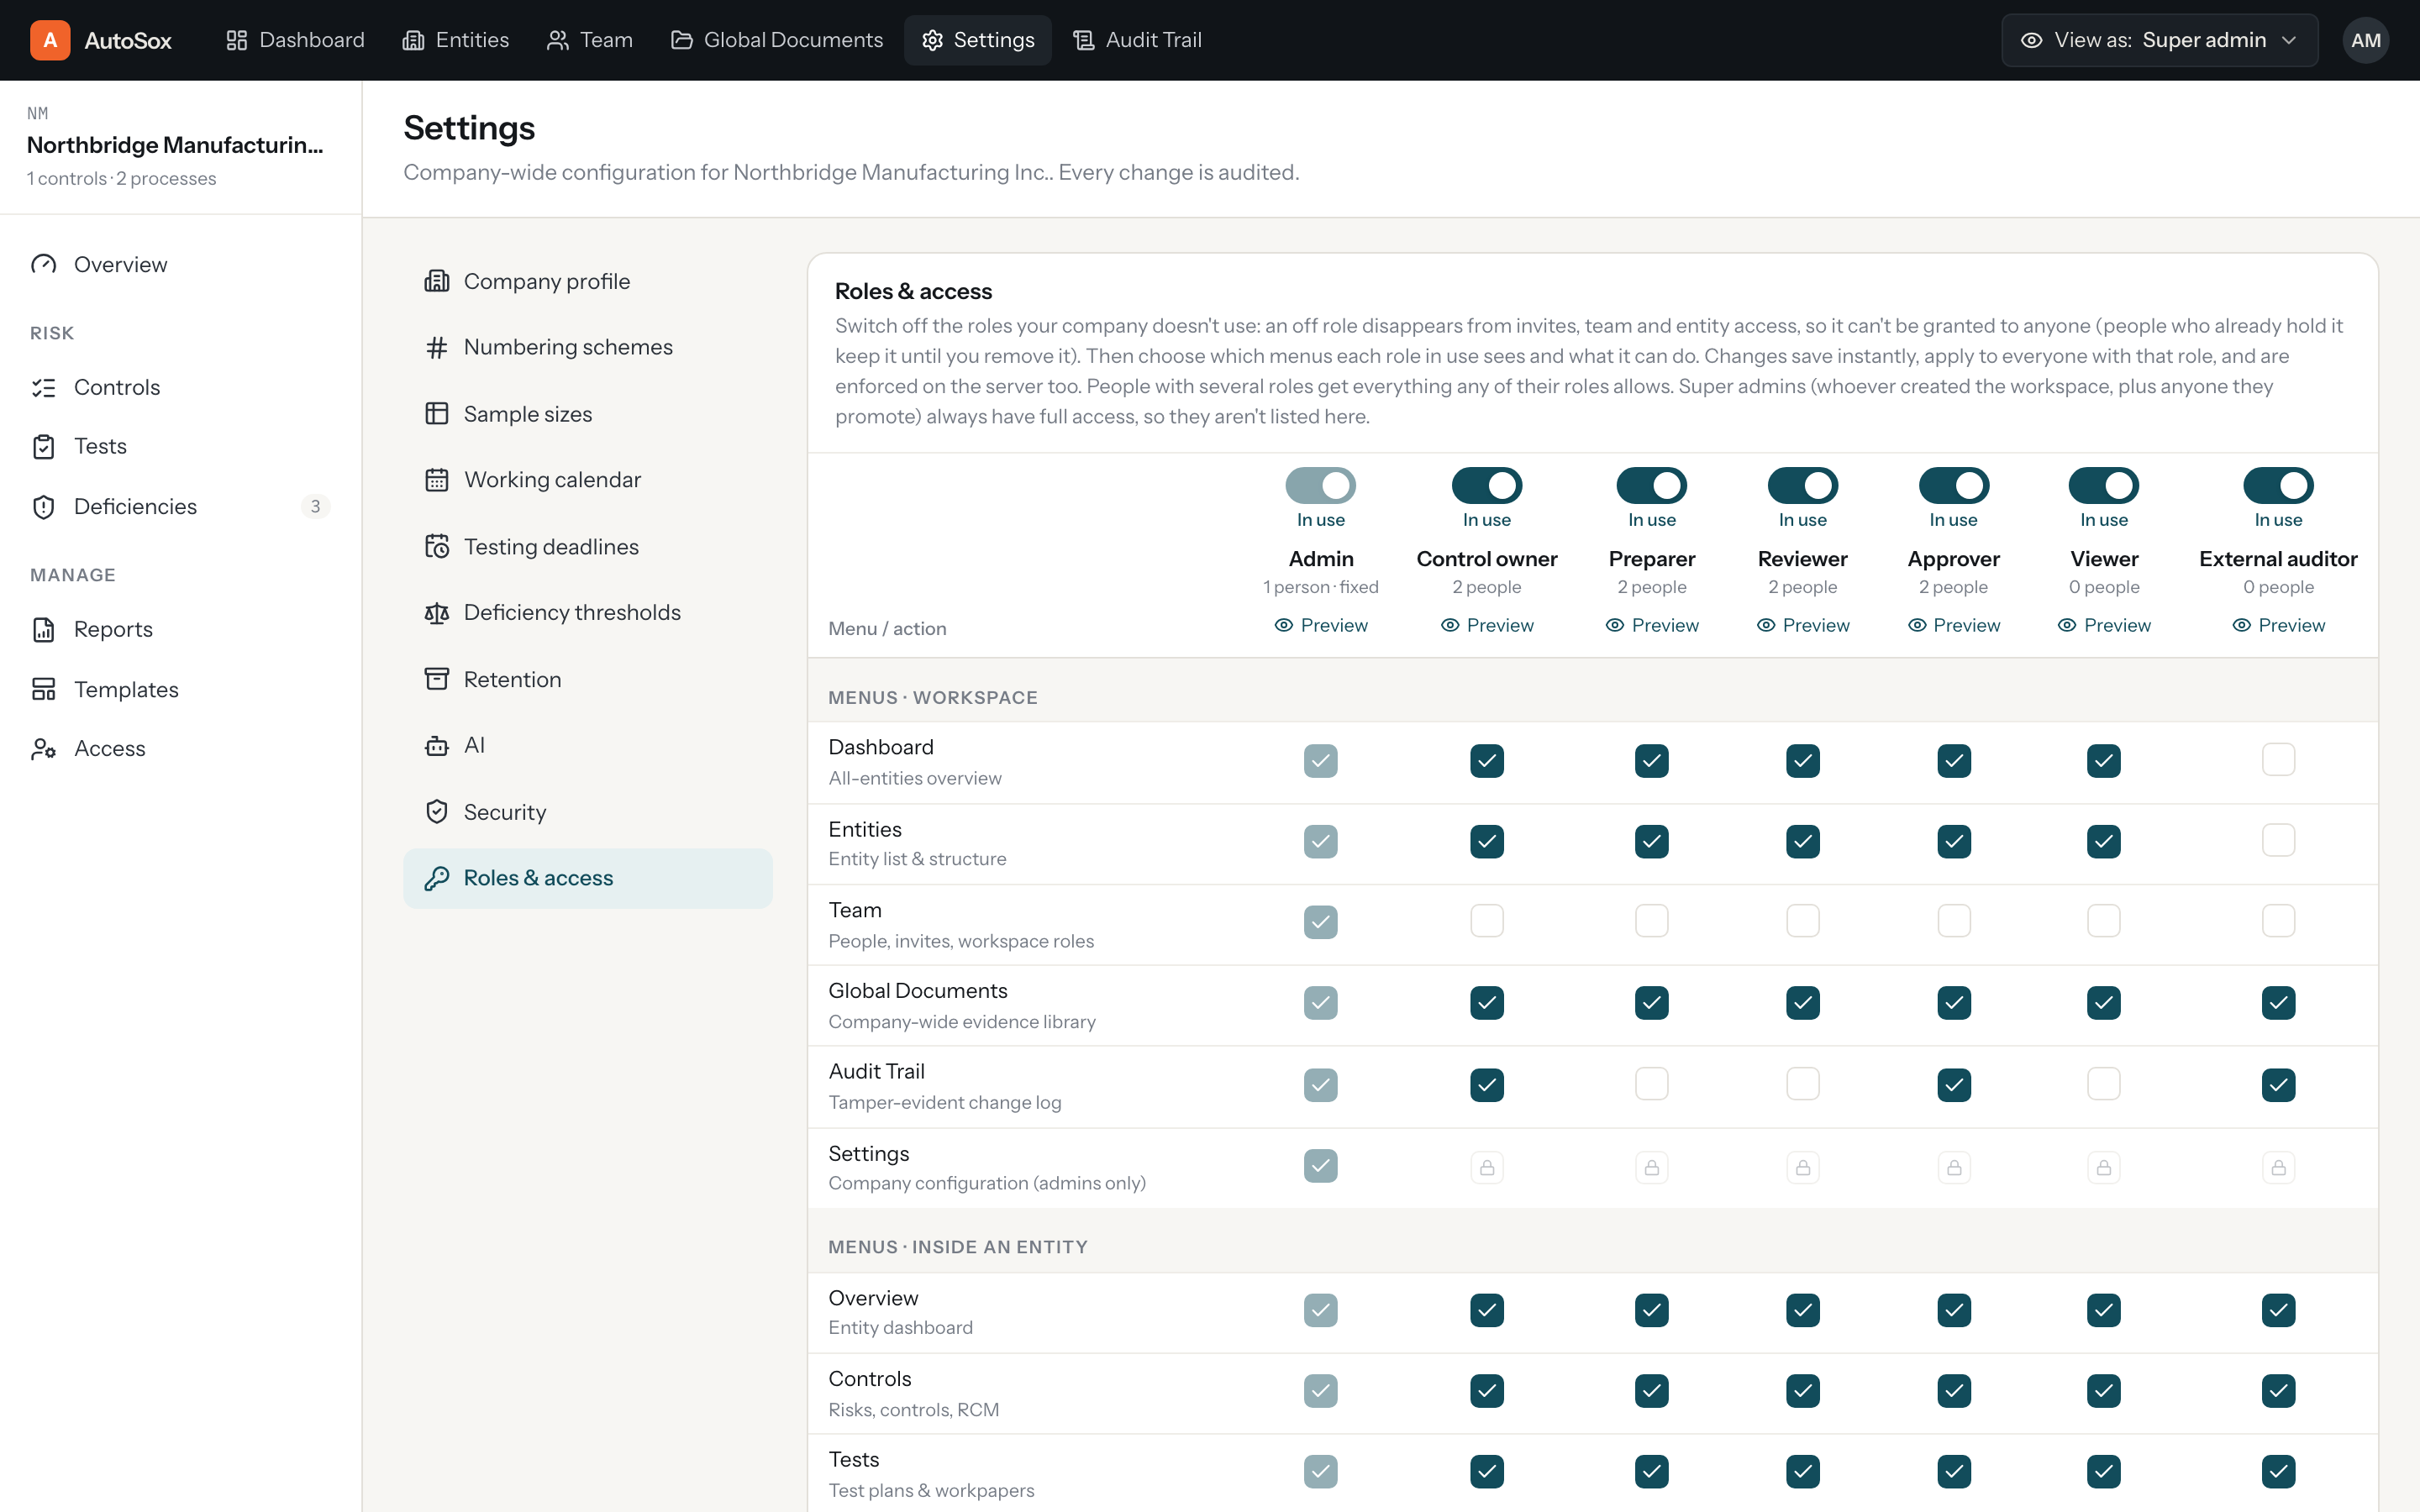
Access and roles
Role-based access with per-entity scoping. External auditors are kept read-only. Live segregation-of-duties checks warn when one person would hold conflicting roles.
Audit trail
An append-only, hash-chained audit log records who changed what, when, and why, with one-click integrity verification.
Evidence integrity
Uploaded evidence is fingerprinted with SHA-256, so a file can be verified against what was actually tested.
File storage
Evidence is kept in private storage and served only through short-lived, signed download links, not public URLs.
Data retention
Retention is configurable per workspace in company settings, rather than fixed by the platform.
MFA policy
Admins and approvers who have not turned on multi-factor authentication are flagged for follow-up.
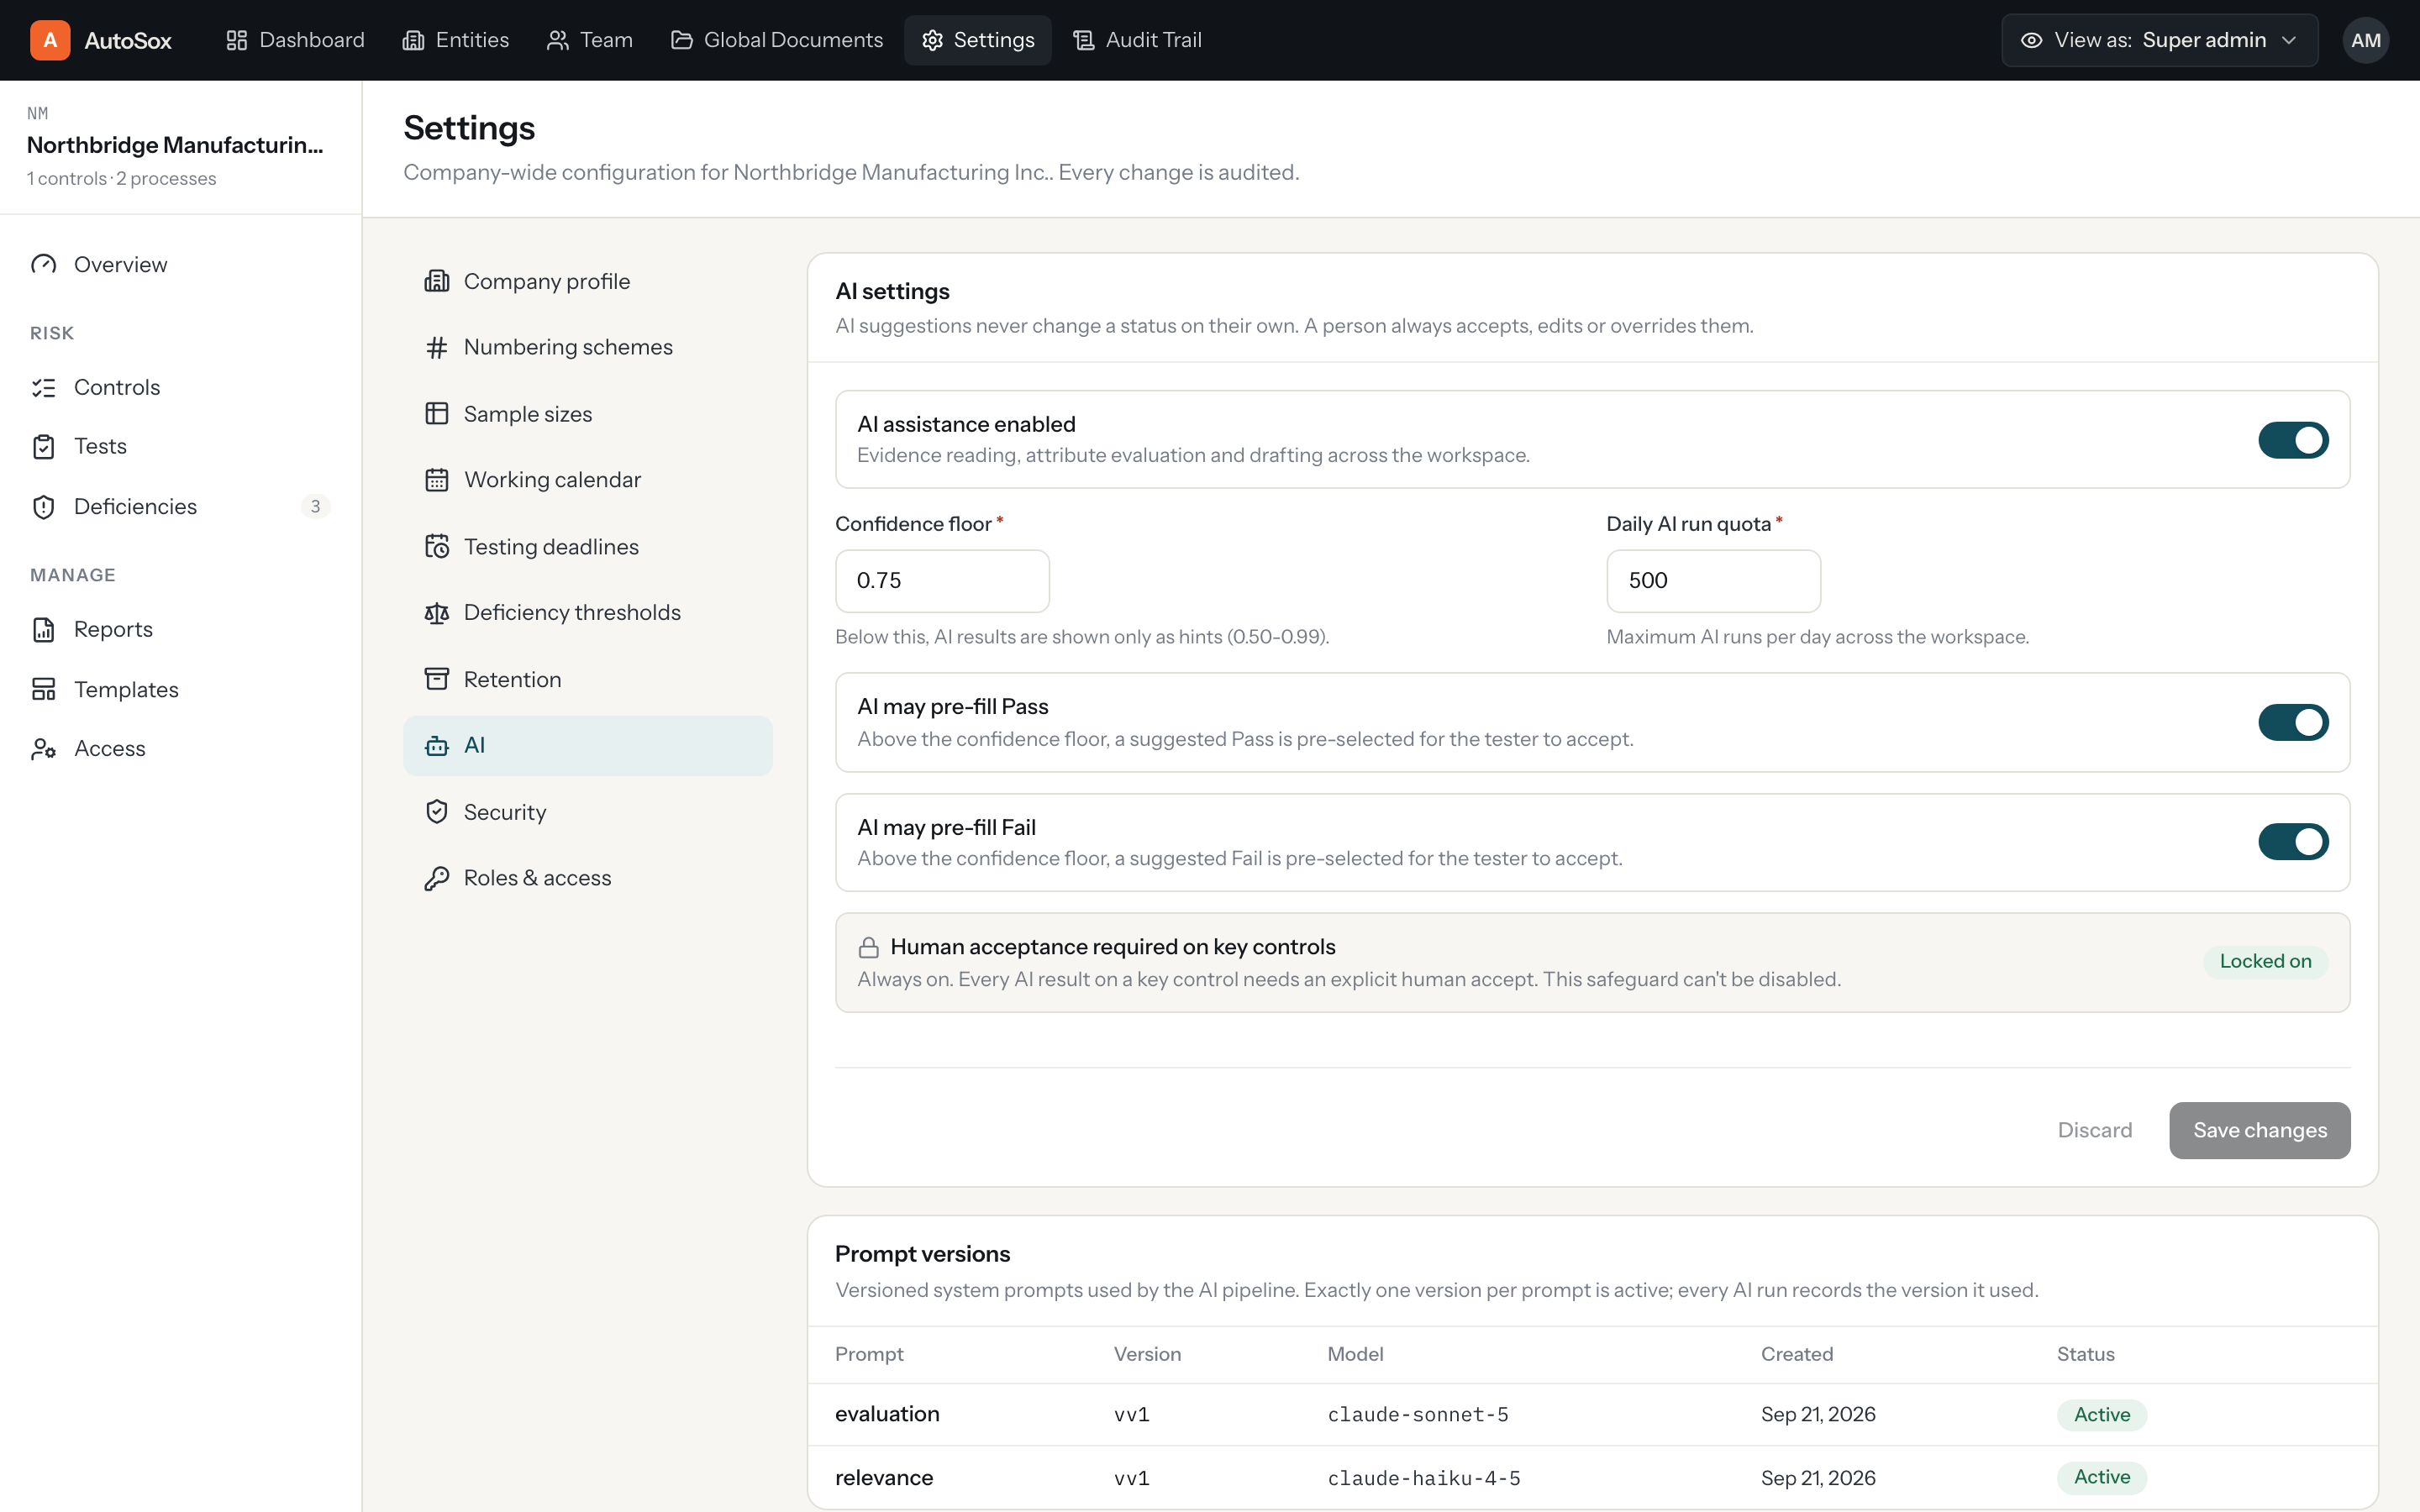
AI AND EVIDENCE
Evidence is treated as data, not instructions.
The AI reads evidence to test attributes; it does not follow instructions embedded inside a document. During testing, a document contained an embedded "system note" telling the reviewer to mark everything Pass. SOXLayer flagged it as a prompt injection attempt and ignored it.
Start your 14-day free trial.
Bring one control and its evidence. See the AI test it in minutes.